
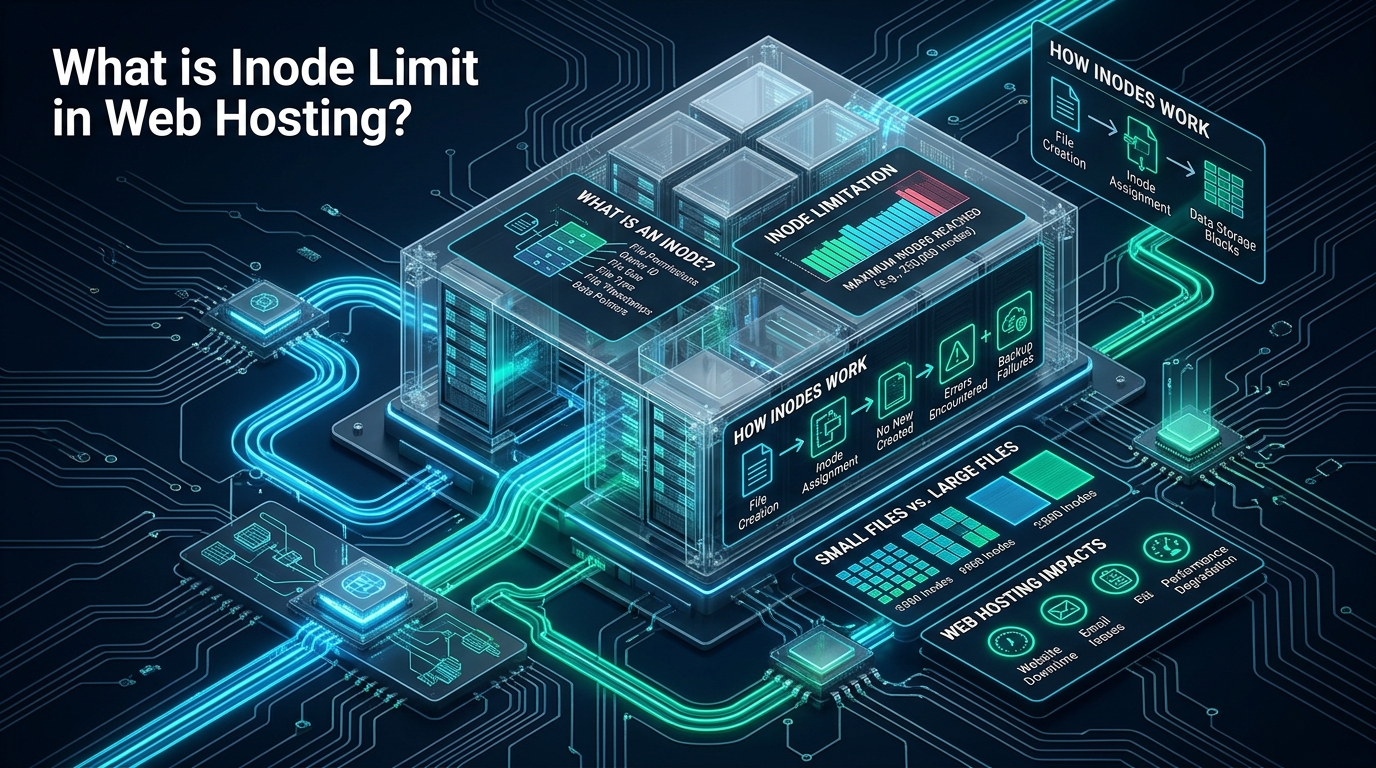
Few infrastructure failures are as baffling to system administrators and web developers as the dreaded “No space left on device” (POSIX ENOSPC / errno 28) error thrown while modern monitoring tools report dozens of gigabytes of unallocated disk storage. This paradoxical operational lockout occurs when an account or filesystem reaches its allocated inode ceiling, halting database transactions, session serialization, and application file creation even across high-performance arrays like those powered by MeraHost. Understanding how POSIX filesystems index data structures, why hosting providers enforce strict inode quotas, and how to programmatically profile and remediate file exhaustion is foundational to maintaining enterprise uptime.
What is an Inode Limit in Web Hosting? Direct Architectural Definition
Definitive Answer: An inode limit in web hosting is the maximum threshold of individual filesystem metadata structures allocated to an account or virtual server. Because every single file, directory, symlink, and socket requires exactly one inode regardless of file size, exhausting this limit prevents all subsequent file writes and crashes web applications despite ample gigabytes of remaining disk capacity.
In POSIX-compliant operating systems—including Linux distributions powering modern web infrastructure such as AlmaLinux, CloudLinux, Debian, and Ubuntu—the file storage model is strictly partitioned into two distinct primitives: data storage blocks (where file payload contents reside) and index nodes (commonly known as inodes), which store the metadata and structural pointers for every file system object.
When a web hosting provider assigns a plan with “50 GB Storage and 250,000 Inodes”, they are applying a dual-constraint resource quota. If your site creates 250,000 files that each measure merely 1 KB (consuming only 250 MB of raw disk capacity), your hosting account has reached 100% of its inode allowance. From that precise moment, any PHP script, database background worker, email daemon, or CMS plugin attempting to write a new file will fail immediately with an I/O error.
Architecture Note: Inodes do not store the filename or path of a file. In UNIX architecture, a directory is simply a special file containing a table that maps human-readable string names to corresponding numerical inode identifiers. Multiple directory entries (dentries) can point to the exact same inode via hard links, sharing the identical underlying storage blocks and metadata record.
Deep Dive: What Is Stored Inside an Inode Structure?
To understand why inodes introduce substantial operating system and memory overhead, one must inspect what the Linux Virtual File System (VFS) and the underlying filesystem driver (such as ext4, XFS, or ZFS) pack into each inode. On standard modern 64-bit Linux ext4 installations, each inode occupies 256 bytes on disk (and dynamic structs in RAM). It tracks:
- File Mode & Type: Permissions (read, write, execute masks) and object type (regular file, directory, symbolic link, socket, named pipe FIFO, block device, or character device).
- Ownership Identifiers: The numerical User ID (
UID) and Group ID (GID) that own the resource. - Physical Byte Count & Block Allocations: The exact file size in bytes, along with the count of 512-byte sectors assigned to the object.
- POSIX Timestamps: Access time (
atime), modification time (mtime), inode metadata change time (ctime), and file creation / birth time (crtimeorbtime). - Link Count: The number of directory hard links referencing this specific inode number. When this count reaches zero and no open file descriptors hold it, the kernel reclaims the data blocks and marks the inode free in the allocation bitmap.
- Extended Attributes (xattr) & Access Control Lists (ACLs): Security labels (SELinux contexts), immutable flags (
chattr +i), and granular POSIX ACL permissions. - Data Block Addressing / Extent Tree: In modern ext4, an extent tree maps contiguous physical disk blocks to logical file offsets, reducing pointer fragmentation compared to legacy indirect block arrays.
You can inspect the exact inode metadata of any file directly from the Linux command line using the stat utility:
# Inspecting physical inode details of a WordPress configuration file
$ stat /home/customer/public_html/wp-config.php

  File: /home/customer/public_html/wp-config.php
  Size: 3240       	Blocks: 8          IO Block: 4096   regular file
Device: 801h/2049d	Inode: 14421892    Links: 1
Access: (0640/-rw-r-----)  Uid: ( 1002/customer)   Gid: ( 1002/customer)
Access: 2026-10-24 04:12:30.491823019 +0000
Modify: 2026-10-20 18:30:15.119284001 +0000
Change: 2026-10-20 18:30:15.119284001 +0000
 Birth: 2026-10-20 18:30:15.119284001 +0000
Why Hosting Providers Enforce Inode Quotas: The Systems Engineering Reality
Many non-technical users assume hosting providers limit inodes merely as a commercial upsell tactic to force account upgrades. However, from the perspective of enterprise Linux hosting engineering, unbounded inode growth is a severe architectural vulnerability that can cripple hardware performance, degrade hypervisor responsiveness, and exhaust kernel memory.
1. Linux Kernel SLAB Cache and VFS Dentry Saturation
Whenever the operating system reads or checks a file, the Linux VFS creates two in-memory kernel structures: an inode struct and a dentry (directory entry) struct. These live inside non-swappable kernel SLAB/SLUB memory caches (specifically dentry, ext4_inode_cache, or xfs_inode). When an unconstrained tenant spawns 2,000,000 tiny cache or session files, the server’s RAM is rapidly consumed by millions of cached metadata pointers, triggering high kernel kswapd CPU churn, memory compaction stalls, and I/O wait spikes.
2. Catastrophic Backup and Replication Degradation
Backing up a single 20 GB compressed database archive across a PCIe Gen4 NVMe array takes under 8 seconds at sequential read speeds exceeding 3,500 MB/s. Conversely, backing up 20 GB composed of 1,500,000 microscopic cache files requires 1.5 million distinct metadata lookups, inode updates, and directory traversals. The sequential throughput collapses into pure random 4KB I/O. A backup routine that should complete in minutes stretches into four hours, saturating storage controller queue depths and degrading service quality for every neighbor on the hypervisor.
3. Filesystem Consistency Check (fsck) Recovery Latency
In the event of an unscheduled hardware reboot, enterprise power loss, or storage cluster failover, the storage volume may undergo an e2fsck or xfs_repair scan. The duration of Phase 1 (checking inodes, blocks, and sizes) and Phase 2 (checking directory structure) is directly proportional to the total number of allocated inodes, not the total gigabytes used. A partition with 50,000,000 inodes can take hours to verify, turning a 3-minute reboot into prolonged downtime.
Architecture Note: CloudLinux and cPanel implement user-level inode controls using Linux kernel disk quota modules (
quota_v2) and LVE (Lightweight Virtual Environment) containers. When an account crosses itssoft limit, a grace period begins; crossing thehard limitimmediately halts system calls such ascreat(),open(O_CREAT),mkdir(), andsymlink().
Hosting Architecture Comparison: Inode Quotas and Filesystem Behavior
The table below illustrates how different tiers of hosting architecture handle inode quotas, filesystem overhead, and performance implications across typical enterprise environments:
| Hosting Tier / Architecture | Typical Inode Quota | Underlying Filesystem | Enforcement Mechanism | Backup / IOPS Impact |
|---|---|---|---|---|
| Budget Shared Hosting | 100,000 – 150,000 | ext4 / NFS Mounts | Hard OS User Quota | High I/O Throttling |
| Standard Cloud / cPanel | 250,000 – 400,000 | ext4 with quota_v2 | LVE / CloudLinux Quota | Moderate Random I/O |
| MeraHost Enterprise NVMe | 600,000 – Unlimited* | Optimized XFS / Pure NVMe | Dynamic Resource Pools | Zero Throttling (Pure NVMe) |
| Dedicated Cloud VPS | Full Filesystem Allocation | XFS / ZFS pool (zfs-on-linux) | Self-Managed / Sysctl | Direct Hardware Bound |
The 5 Primary Culprits Behind Inode Exhaustion in Web Applications
When web applications breach their inode boundaries, the culprit is almost never legitimate user documents or source code files. Instead, inode bloat is overwhelmingly driven by automated background processes accumulating unpruned ephemeral records:
1. Abandoned PHP Session Files
By default, PHP file-based session handling writes individual text files (e.g. sess_2f7d337b8e874a9e9d4d47866e) into /tmp or the user’s private session directory. On high-traffic e-commerce or community portals with crawlers and bots hitting non-cached endpoints, thousands of unique sessions are spawned hourly. If PHP’s probabilistic garbage collection (session.gc_probability / session.gc_divisor) is disabled or broken, directories frequently accumulate 500,000 to over 2,000,000 orphaned session files.
2. Static Page Caching Plugins (WordPress / Magento / Drupal)
Plugins such as WP Super Cache, W3 Total Cache, or basic file-based caching systems generate pre-rendered static HTML and gzipped payloads for every visited URL variant. When query string URLs (from marketing UTM tags, faceted eCommerce filters, or referrer tracking) are cached indiscriminately, a single product catalog with 1,000 items can explode into 300,000 static cache files within weeks.
3. Catch-All Email Inboxes and Spam Spikes
Standard Linux mail delivery agents (Dovecot / Exim) store incoming emails using the Maildir format. In Maildir, every single message received is saved as a discrete file inside ~/mail/domain.com/user/cur/ or new/. A domain with a catch-all email address receiving dictionary attacks or an unmonitored mailbox can easily stockpile 400,000 spam emails, completely freezing web services.
4. Multi-Size Image Thumbnail Generation
Whenever an image is uploaded to WordPress, the core media engine and the active theme generate multiple scaled renditions (thumbnail, medium, large, 2x retina, mobile, square crop). Modern themes often register 10 to 15 distinct image sizes. If an eCommerce store uploads 20,000 product photos, the media library generates over 300,000 physical files on disk.
5. Unpruned Build Artifacts and Development Debris
Staging deployments, automated CI/CD runners, and neglected Node.js or Composer dependencies are notorious inode drains. A single node_modules directory from a modern frontend build framework commonly contains 40,000 to 70,000 micro-files. Leaving three abandoned staging backups or development directories instantly devours 200,000 inodes.
Production Diagnostics: High-Performance CLI Commands to Find Inode Hogs
When an account suffers an inode freeze, naive diagnostic commands like ls -lR or find . | wc -l will frequently hang the terminal or trigger out-of-memory errors due to millions of nested dentry entries. Enterprise sysadmins rely on optimized one-liners designed for rapid traversal:
# Step 1: Verify filesystem-wide inode usage across all mountpoints
$ df -ih

# Step 2: Check user-specific quota on cPanel / CloudLinux servers
$ quota -s customer

# Step 3: Top-level directory inode audit (scans current directory depth 1)
$ find . -maxdepth 1 -mindepth 1 -type d | while read dir; do \
    echo -n "$dir: "; find "$dir" | wc -l; \
  done | sort -n -k 2

# Step 4: Ultra-fast perl/awk directory scanner for high-density folders
$ find /home/customer/ -maxdepth 2 -type d -exec bash -c 'echo -n "{}: "; find "{}" -type f | wc -l' \; | sort -n -k 2 -r | head -n 15
If you discover a directory containing 400,000 orphaned session files, running rm -f sess_* will immediately abort with the POSIX error -bash: /bin/rm: Argument list too long (errno E2BIG) because the shell expansion exceeds ARG_MAX. Instead, stream the filenames directly to find -delete or pipeline through xargs:
# Safe, high-speed deletion of millions of small files without shell buffer overrun
$ find /home/customer/tmp/ -name "sess_*" -type f -delete

# Alternative memory-efficient deletion using xargs with multithreading
$ find /home/customer/cache/ -type f -print0 | xargs -0 -P 4 -n 1000 rm -f
Real Production Configuration Files & Automation
To permanently prevent inode exhaustion, enterprise production servers must deploy automated systemd timers for session pruning, alongside optimized kernel VFS cache tuning to maintain high-speed dentry reclamation.
1. Kernel VFS Cache & Inode Tuning: /etc/sysctl.d/99-filesystem-inodes.conf
This configuration optimizes how aggressively the Linux kernel reclaims inode and dentry caches from RAM and expands system-wide file descriptor capacities to prevent socket starvation:
# /etc/sysctl.d/99-filesystem-inodes.conf
# Enterprise Linux Filesystem & VFS Cache Optimization

# Control aggressiveness of kernel inode and dentry cache reclaiming (default 100).
# A setting of 50 retains dentries in memory longer for high-speed repeated web reads,
# while preventing runaway kernel memory consumption.
vm.vfs_cache_pressure = 50

# Expand system-wide file allocation table maximums for high-density environments
fs.file-max = 2097152

# Protect inotify watchers from exhaustion across heavy CMS installations
fs.inotify.max_user_watches = 524288
fs.inotify.max_user_instances = 1024

# Increase dirty background ratios to smooth out writeback burst I/O on NVMe
vm.dirty_background_ratio = 5
vm.dirty_ratio = 10
2. Automated PHP Session Cleanup: Systemd Service & Timer Units
Rather than relying on uncoordinated web requests or unreliable cron scripts, production systems utilize systemd units to purge expired session files directly from storage:
# /etc/systemd/system/php-session-cleanup.service
[Unit]
Description=Clean Up Stale PHP Session Inodes
After=local-fs.target

[Service]
Type=oneshot
ExecStart=/usr/bin/find /var/cpanel/php/sessions/ -type f -name "sess_*" -mmin +1440 -delete
Nice=19
IOSchedulingClass=idle

# /etc/systemd/system/php-session-cleanup.timer
[Unit]
Description=Run PHP Session Cleanup Hourly
RefuseManualStart=no
RefuseManualStop=no

[Timer]
OnCalendar=*-*-* *:15:00
Persistent=true

[Install]
WantedBy=timers.target
Architecture Note: When managing mission-critical databases and microservices, migrating session storage from local filesystems to in-memory Redis or Memcached instances completely eliminates filesystem inode overhead for session persistence, unlocking sub-millisecond retrieval speeds.
Frequently Asked Questions (Native Accordion FAQs)
Can I increase the inode limit on a live Linux ext4 filesystem?
On an existing ext4 filesystem, the total number of inodes is fixed at the moment the volume is created using mkfs.ext4 -i bytes-per-inode. Once formatted, you cannot dynamically increase the inode table without backing up your data, re-formatting the block device with a smaller bytes-per-inode ratio, and restoring files. In contrast, modern filesystems like XFS allocate inodes dynamically across allocation groups as the volume expands, eliminating static inode limits at the storage partition level.
What happens to my website immediately when the inode quota reaches 100%?
When your inode limit is exhausted, all Linux write system calls that require creating a new file or directory immediately return EDQUOT (Disk quota exceeded) or ENOSPC. Common symptoms include: WordPress showing “Uploads folder is not writable”, inability to create or save new blog posts, MySQL/MariaDB crashing because it cannot allocate temporary sorting tables, incoming emails bouncing back to senders, and site caching plugins failing silently.
Does deleting a 10 GB file free up more inodes than deleting a 1 KB file?
No. Deleting a single 10 GB file releases 10 GB of data blocks, but only exactly one inode. Conversely, deleting 10,000 tiny 1 KB files releases 10,000 inodes while freeing only ~10 MB of disk space. When diagnosing an inode ceiling issue, your objective is to eliminate the total count of files, not their cumulative byte weight.
How can WordPress sites reduce their overall inode footprint permanently?
To permanently optimize WordPress inode usage: (1) disable unused image thumbnail sizes in your active theme or via add_filter('intermediate_image_sizes_advanced', ...), (2) transition from disk-based caching plugins to server-level object caching using Redis or LiteSpeed LSCache, (3) configure automated cron tasks to delete expired transient records from the wp_options database table, and (4) store media assets on S3-compatible cloud object storage rather than local web storage.
When scaling enterprise e-commerce portals, SaaS platforms, or high-concurrency client clusters, overcoming artificial file count throttling is essential. Transitioning to dedicated, high-quota infrastructure on MeraHost Enterprise Cloud gives your mission-critical applications pure Enterprise NVMe speeds, generous inode allowances, and LiteSpeed Web Server acceleration with no surprise price escalations.
Deploy Enterprise-Grade Production Infrastructure
Need guaranteed performance with zero price hikes? Host mission-critical workloads on MeraHost with pure Enterprise NVMe, LiteSpeed Web Server, and Same Renewal Price, Always (starting at ₹99/mo).