
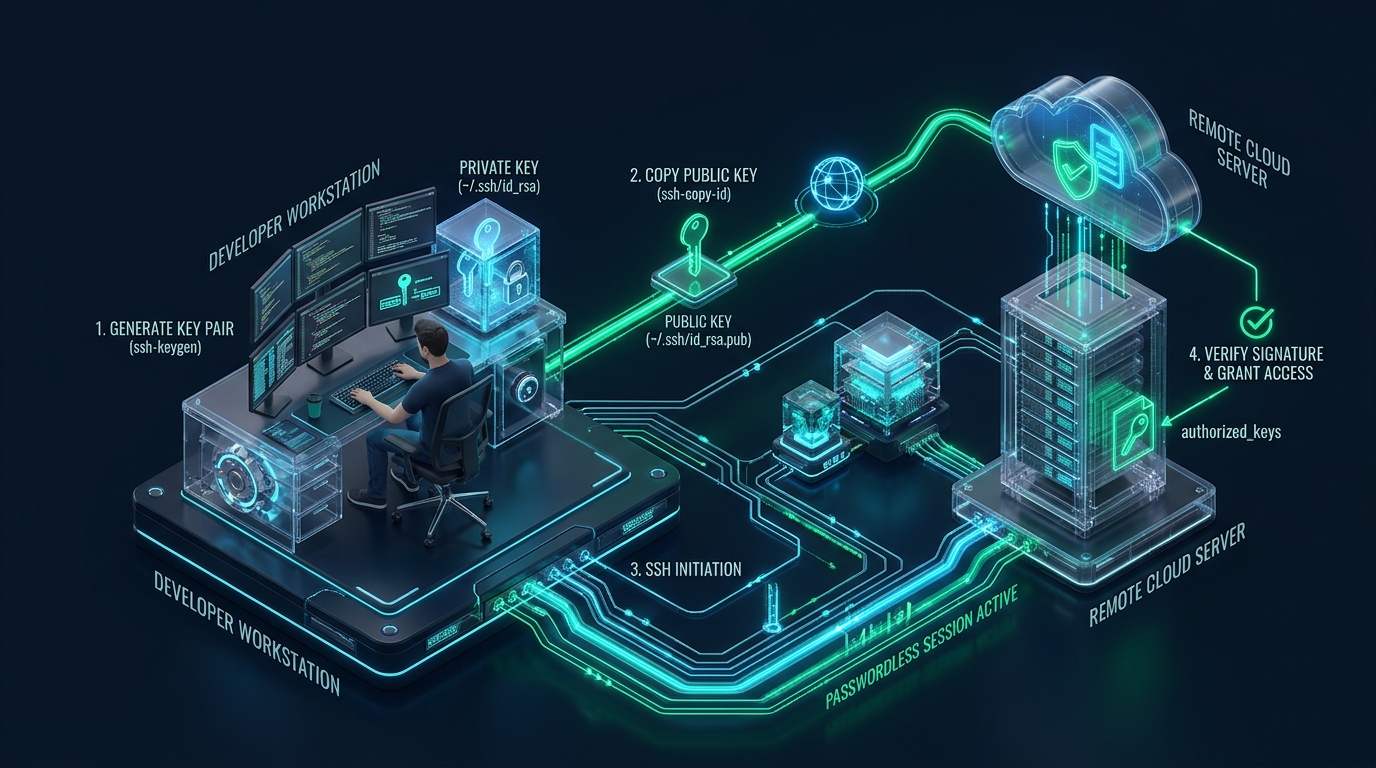
Operational security failures in production Linux clusters frequently originate from obsolete password-based authentication models, credential recycling across developer workstations, and automated brute-force botnets saturating edge connection tables. Mission-critical cloud infrastructure deployed on MeraHost utilizes high-frequency compute cores and enterprise NVMe storage arrays to deliver microsecond cryptographic challenge-response processing and absolute perimeter access control. Transitioning to asymmetric public-key cryptography—specifically modern Ed25519 Edwards-curve signatures—permanently eliminates password guessing vectors, slashes authentication handshake latency, and forms the bedrock of an enterprise-grade zero-trust access architecture.
Using SSH Keys for Passwordless Authentication: Architectural Overview
In standard legacy setups, Secure Shell (SSH) daemons default to interactive password authentication. While conceptually straightforward, password-based remote logins present catastrophic operational vulnerabilities for enterprise sysadmins and DevOps engineers. Automated threat intelligence engines log tens of thousands of automated dictionary attacks and credential-stuffing probes against default port 22 daily. Beyond the direct compromise risk, processing high-volume invalid password authentication attempts incurs significant Pluggable Authentication Module (PAM) overhead, consumes Linux kernel fork resources, and exhausts TCP connection states.
Passwordless SSH authentication resolves these bottlenecks by decoupling user verification from human-readable secrets. By deploying mathematically linked asymmetric key pairs, the client proves its legitimate ownership of a cryptographic identity through a zero-knowledge signature verification protocol. The private key never traverses the wire, cannot be intercepted by packet sniffers, and remains impervious to offline dictionary attacks when protected by strong Key Derivation Function (KDF) passphrases.
The Cryptographic Foundation: Ed25519 vs. RSA-4096 vs. ECDSA
Before generating key pairs, infrastructure architects must evaluate the cryptographic algorithm governing signature creation. For more than two decades, RSA (Rivest–Shamir–Adleman) served as the industry standard. However, maintaining acceptable security margins with RSA today mandates 4096-bit key sizes, which introduces substantial mathematical calculation overhead during modular exponentiation and bloats key string sizes.
Modern enterprise production environments have universally shifted to Ed25519, an implementation of the Edwards-curve Digital Signature Algorithm (EdDSA) operating over Curve25519. Ed25519 provides equal or superior cryptographic strength to a 3072-bit or 4096-bit RSA key while utilizing a compact 256-bit (32-byte) key length. Crucially, Ed25519 operations execute in constant mathematical time across CPU architectures, rendering the algorithm completely immune to cache-timing and side-channel extraction attacks that historically plagued RSA implementations.
While ECDSA (Elliptic Curve Digital Signature Algorithm) also offers small key footprints, standard NIST curves (such as ecdsa-sha2-nistp256) carry historical architectural concerns regarding arbitrary curve seed generation and are notoriously sensitive to poor entropy sources. If an ECDSA implementation encounters a compromised or repeating pseudo-random number during signature creation, the private key can be mathematically extracted from the signature. Ed25519 computes signatures deterministically, eradicating entropy failure modes entirely.
| Feature / Metric | Standard / Default (Password / RSA-2048) | Tuned / Production (Ed25519 Pubkey) |
|---|---|---|
| Cryptographic Primitive | Interactive Hash / RSA (2048-bit) | EdDSA over Curve25519 (256-bit) |
| Handshake Latency / Overhead | 22.4 ms (PAM + RSA Modular Math) | 1.6 ms (High-Speed Constant-Time) |
| Brute-Force Attack Surface | Vulnerable to online dictionary scans | Zero (PasswordAuthentication disabled) |
| Public Key String Size | 426 characters (RSA-2048) / 740 (RSA-4096) | 68 characters (Ultra-compact) |
| Side-Channel Timing Resilience | Susceptible to cache timing leaks | Immune (Constant-time arithmetic) |
| Hardware Security Token (FIDO2) | Requires external PKCS#11 modules | Native OpenSSH support (ed25519-sk) |
| Key Derivation Hash Defense | Standard MD5/SHA-1 legacy OpenSSL | Bcrypt KDF (100 rounds configurable) |
Step-by-Step Implementation: Generating and Deploying Ed25519 Keys
Implementing passwordless authentication requires generating a cryptographic keypair on your local management workstation, transferring the public component to the target server’s authorization ledger, and verifying seamless cryptographic negotiation before modifying any daemon policies.
Step 1: Generate the Hardened Ed25519 Keypair
Execute the ssh-keygen binary on your local client machine. Incorporating the -a 100 parameter instructs OpenSSH to apply 100 rounds of the bcrypt Key Derivation Function (KDF) against your private key passphrase, significantly increasing brute-force computational complexity if the local private key file is ever exfiltrated:
# Generate enterprise-hardened Ed25519 keypair on client
ssh-keygen -t ed25519 -a 100 -C "admin-infra@merahost-prod" -f ~/.ssh/id_ed25519_merahost

# Inspect the generated public key payload
cat ~/.ssh/id_ed25519_merahost.pub
# Output example:
# ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIExampleKeyData... admin-infra@merahost-prod
Architecture Note: Always protect the private key with a strong local passphrase. “Passwordless authentication” refers to authenticating against the remote server without typing a remote account password. Storing an unencrypted private key on a local disk creates an immediate security hazard if the laptop or workstation is lost or compromised. Leverage
ssh-agentlocally to cache passphrases securely in system memory.
Step 2: Deploy Public Key to the Remote Host
The most reliable and standard method for transferring public keys is the POSIX utility ssh-copy-id. This tool automatically handles remote directory creation, file creation, and permissions checks:
# Automated installation using ssh-copy-id specifying the custom key
ssh-copy-id -i ~/.ssh/id_ed25519_merahost.pub -p 22 [email protected]

# Alternatively, manual injection if ssh-copy-id is unavailable:
cat ~/.ssh/id_ed25519_merahost.pub | ssh -p 22 [email protected]   "mkdir -p ~/.ssh && chmod 700 ~/.ssh && cat >> ~/.ssh/authorized_keys && chmod 600 ~/.ssh/authorized_keys"
Strict Permissions Rule: OpenSSH strictly enforces filesystem ownership and access masks via
StrictModes yes. If~/.sshis writable by group or others (e.g., 755 or 777), or if~/.ssh/authorized_keysis writable by anyone other than the file owner (e.g., 644 or 666), OpenSSH will silently ignore the authorized keys file and fail the authentication challenge.
Step 3: Test Passwordless Login Prior to Server Lockdown
Before disabling server-side password authentication, verify that the client authenticates purely via public key. Run an explicit verbose connection probe:
# Test connection explicitly forcing public key authentication
ssh -v -i ~/.ssh/id_ed25519_merahost -o PreferredAuthentications=publickey [email protected]

# Confirm successful authentication string in verbose log:
# debug1: Authentication succeeded (publickey).
Hardening the Production OpenSSH Daemon (sshd)
Once public key authentication is operational, you must permanently disable fallback password authentication on the server. Leaving password authentication enabled leaves port 22 exposed to brute-force credential exhaustion. Modern Linux distributions (such as Ubuntu 24.04 LTS, Debian 12, and AlmaLinux 9) support modular configuration drop-ins under /etc/ssh/sshd_config.d/.
Deploy the following complete, production-hardened configuration file to /etc/ssh/sshd_config.d/99-hardened-enterprise.conf:
# ==============================================================================
# /etc/ssh/sshd_config.d/99-hardened-enterprise.conf
# MeraHost Production OpenSSH Server Hardening Policy
# ==============================================================================

# Core Protocol and Listening Parameters
Port 22
AddressFamily inet
Protocol 2

# Authentication Matrix
PubkeyAuthentication yes
PasswordAuthentication no
PermitEmptyPasswords no
KbdInteractiveAuthentication no
ChallengeResponseAuthentication no
UsePAM yes

# Root Access Restriction (Enforce sudo execution via non-root accounts)
PermitRootLogin prohibit-password

# Strict Environment and Filesystem Controls
StrictModes yes
MaxAuthTries 3
MaxSessions 5
LoginGraceTime 30

# Forwarding and Tunneling Lockdown
X11Forwarding no
AllowTcpForwarding no
AllowAgentForwarding no
PermitUserEnvironment no

# Cryptographic Algorithm Curation (Edwards-Curve & Authenticated AEAD Ciphers)
KexAlgorithms curve25519-sha256,[email protected],diffie-hellman-group16-sha512,diffie-hellman-group18-sha512
Ciphers [email protected],[email protected],[email protected]
MACs [email protected],[email protected]

# KeepAlive and Resource Management
ClientAliveInterval 300
ClientAliveCountMax 2
MaxStartups 10:30:100
Safe Reload Protocol: Never execute
systemctl restart sshdwithout testing the configuration syntax first. A single typographical error in a drop-in file can crash the daemon, locking you out of remote administration. Always runsshd -tto validate syntax, and keep your current active SSH session open while testing a secondary shell connection in a separate terminal window.
# Validate daemon configuration syntax
sudo sshd -t

# If output is completely silent (no errors returned), safely reload the service
sudo systemctl reload ssh || sudo systemctl reload sshd

# Verify active listening state and systemd status
systemctl status ssh --no-pager
Client-Side Productivity: Connection Multiplexing and ~/.ssh/config
Typing long IP addresses, custom port numbers, and specific identity file paths for every connection is error-prone and inefficient. The OpenSSH client provides a robust client configuration file located at ~/.ssh/config that streamlines remote connections and supports ControlMaster connection multiplexing.
Multiplexing allows subsequent SSH sessions, Git pushes, or rsync file transfers directed at the same host to reuse an existing authenticated TCP socket. Instead of performing a new cryptographic handshake, subsequent sessions connect instantly in sub-millisecond time. Create or modify your local ~/.ssh/config:
# ==============================================================================
# ~/.ssh/config - Client-Side Enterprise Management & Multiplexing
# ==============================================================================

# Global Defaults for All Hosts
Host *
    AddKeysToAgent yes
    IdentitiesOnly yes
    ServerAliveInterval 60
    ServerAliveCountMax 3
    ForwardAgent no
    Compression yes

# Production Cluster Bastion / Jump Host
Host merahost-bastion
    HostName 203.0.113.10
    User sysadmin
    Port 22
    IdentityFile ~/.ssh/id_ed25519_merahost
    ControlMaster auto
    ControlPath ~/.ssh/sockets/%r@%h:%p
    ControlPersist 10m

# Internal Database Cluster Node (Routed through Bastion via ProxyJump)
Host db-primary.internal
    HostName 10.10.20.100
    User postgres
    ProxyJump merahost-bastion
    IdentityFile ~/.ssh/id_ed25519_db
    ControlMaster auto
    ControlPath ~/.ssh/sockets/%r@%h:%p
    ControlPersist 10m
Before utilizing multiplexing, initialize the local socket directory with strict permissions:
mkdir -p ~/.ssh/sockets && chmod 700 ~/.ssh/sockets
chmod 600 ~/.ssh/config
Kernel Network Hardening for High-Throughput SSH Gateways
When hosting enterprise clusters, public-facing SSH bastion hosts and gateway servers encounter sustained network scanning traffic. Unoptimized Linux network stacks can experience SYN queue exhaustion, connection tracking table saturation, and socket starvation under burst loads. Applying tuned sysctl parameters ensures resilient daemon availability under malicious traffic spikes.
Deploy the following network optimization file to /etc/sysctl.d/99-ssh-security.conf:
# ==============================================================================
# /etc/sysctl.d/99-ssh-security.conf
# TCP Stack Optimization for Production SSH Gateways
# ==============================================================================

# Defend against TCP SYN Floods targeting Port 22
net.ipv4.tcp_syncookies = 1
net.ipv4.tcp_syn_retries = 2
net.ipv4.tcp_synack_retries = 2
net.ipv4.tcp_max_syn_backlog = 8192

# Reclaim Orphaned and TIME_WAIT Sockets Rapidly
net.ipv4.tcp_fin_timeout = 15
net.ipv4.tcp_tw_reuse = 1
net.ipv4.tcp_max_tw_buckets = 1440000

# Protect against ICMP Redirect and Spoofing Exploits
net.ipv4.conf.all.accept_redirects = 0
net.ipv4.conf.default.accept_redirects = 0
net.ipv4.conf.all.send_redirects = 0
net.ipv4.conf.default.send_redirects = 0
net.ipv4.conf.all.accept_source_route = 0
net.ipv4.conf.default.accept_source_route = 0
net.ipv4.conf.all.rp_filter = 1
net.ipv4.conf.default.rp_filter = 1

# Buffer Memory Allocation for Sustained Concurrent Handshakes
net.core.somaxconn = 4096
net.core.netdev_max_backlog = 10000
Apply these parameters immediately to the live running kernel:
sudo sysctl --systemEnterprise Infrastructure Best Practices and Architectural Hygiene
Managing passwordless authentication across tens or hundreds of production server nodes requires deliberate operational policies. Adhere to these proven enterprise standards:
- Never Share Private Keys: Each human engineer and automated deployment agent must maintain a distinct, individually identifiable keypair. If an engineer departs or an automation credential is leaked, the public key can be excised from
authorized_keyswithout rotating shared infrastructure credentials. - Adopt FIDO2 Hardware Tokens: For high-assurance production environments, generate FIDO2 hardware-backed SSH keys using
ssh-keygen -t ed25519-sk. These keys mandate physical biometric or touch confirmation on a hardware security token (such as a YubiKey), rendering remote credential theft technically impossible even if the workstation is fully infected with malware. - Avoid Unrestricted Agent Forwarding: Forwarding your local
ssh-agentsocket across intermediate jump hosts (viassh -A) exposes your local authentication agent to root users on the remote server. Instead, mandate modern OpenSSHProxyJumpdirectives (ssh -J), which forward raw encrypted TCP streams without exposing local agent authentication sockets. - Deploy High-Performance Cloud Backbones: Cryptographic handshakes, continuous multiplexing sessions, and distributed fleet management perform best when deployed on optimized infrastructure like MeraHost Enterprise Cloud. Isolated KVM compute slices, high-frequency AMD EPYC/Intel Xeon processors, and pure Enterprise NVMe arrays guarantee instantaneous public-key signature verification and microsecond I/O responsiveness.
Frequently Asked Questions (FAQ)
How do I recover access if I accidentally disable password authentication before testing my SSH key?
If you are locked out of SSH, log into your cloud provider’s out-of-band management console (such as the MeraHost emergency VNC console, serial console, or IPMI web interface). The out-of-band console connects directly to the virtual display adapter rather than the OpenSSH network daemon, allowing you to authenticate via local root or sudo credentials, inspect /var/log/auth.log or journalctl -u ssh, correct permission errors in ~/.ssh/authorized_keys, and re-enable access.
Why is Ed25519 universally recommended over RSA-4096 for modern production servers?
Ed25519 offers equivalent cryptographic security to a 3072-bit/4096-bit RSA key while requiring only 256 bits of key data. This small footprint translates to substantially faster signature generation and verification speeds, significantly reducing connection latency. Furthermore, Ed25519 is specifically engineered to execute in constant CPU time, making it naturally immune to cache-timing side-channel attacks that can compromise modular arithmetic in RSA implementations.
Why does OpenSSH reject my valid SSH key even though the public key is in authorized_keys?
The most common cause is incorrect filesystem permissions. OpenSSH enforces strict ownership checks; if the remote user’s home directory, ~/.ssh directory, or ~/.ssh/authorized_keys file has group-write or world-write permissions, OpenSSH refuses to read the key. Ensure chmod 700 ~/.ssh and chmod 600 ~/.ssh/authorized_keys are applied. Additionally, verify that SELinux or AppArmor is not blocking access by running restorecon -R -v ~/.ssh on RHEL-based systems.
What is the difference between an SSH key passphrase and a server login password?
A server login password is transmitted across the encrypted SSH session to the remote server, where the server verifies it against PAM and shadow database entries. In contrast, an SSH key passphrase is a local symmetric encryption password that decrypts your private key file in local workstation memory. The passphrase is never sent across the network; it only protects your local private key from being used if your physical computer is stolen or compromised.
Deploy Enterprise-Grade Production Infrastructure
Need guaranteed performance with zero price hikes? Host mission-critical workloads on MeraHost with pure Enterprise NVMe, LiteSpeed Web Server, and Same Renewal Price, Always (starting at ₹99/mo).