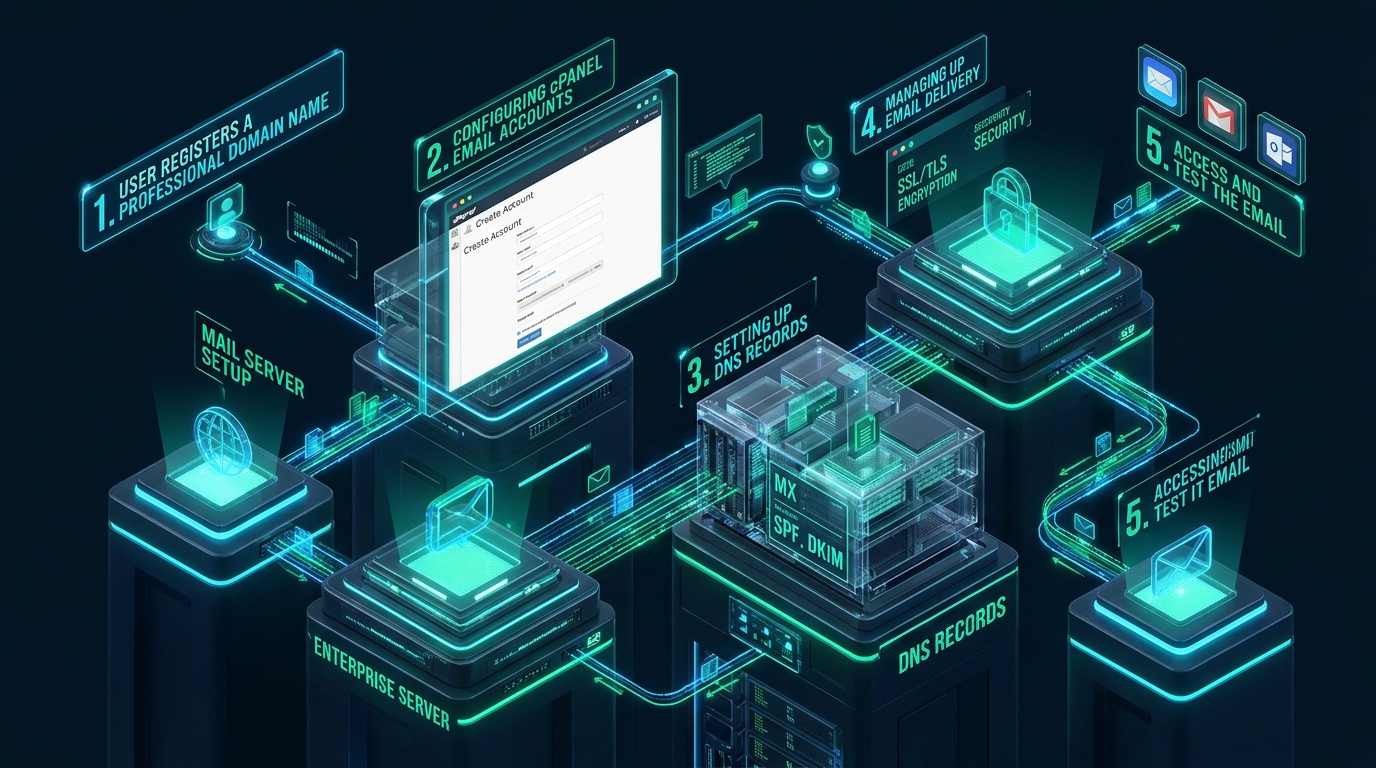
Deploying enterprise-grade business email on cPanel demands a rigorous architectural approach that extends well beyond merely provisioning mailboxes in the graphic user interface. Unhardened mail transfer configurations, missing cryptographic DNS records, and unoptimized mail delivery agents expose corporate domains to pervasive spoofing, aggressive spam filtering, and severe outbound rate-limiting from major recipient clusters such as Google Workspace and Microsoft 365. When hosting business-critical communication channels on MeraHost, implementing deterministic DNS cryptographic alignment, Maildir NVMe storage tuning, and hardened Exim transport queues guarantees near-instantaneous global deliverability and uncompromised inbox placement.
How to Setup Professional Business Email on cPanel: Enterprise Architecture Overview
In contemporary enterprise IT environments, email remains the foundational backbone for identity verification, client correspondence, invoice distribution, and internal audit workflows. Yet, millions of businesses continue to suffer from silent delivery failures—where transactional and corporate emails land directly in the recipient’s spam folder or are rejected at the edge MTA (Message Transfer Agent) without a diagnostic bounce report. The root cause is rarely the email content itself; rather, it stems from architectural shortcomings in reverse DNS delegation, missing cryptographic signatures, suboptimal Dovecot indexing, and unauthenticated outbound SMTP routing.
This authoritative architectural deep dive explores the underlying mechanics of setting up and operating corporate business email infrastructure on cPanel. We examine the transition from legacy transport protocols to secure TLS 1.3 submission, analyze Maildir filesystem layouts on enterprise NVMe arrays, provide complete production configuration templates, and outline the precise DNS records required to achieve a flawless 10/10 deliverability score across global recipient mail servers.
1. The Core Mail Architecture: MTAs, MDAs, and Transport Protocols
To administer a high-availability email environment, systems engineers must first decouple the distinct daemon tiers operating beneath cPanel’s unified management abstraction layer. In a typical cPanel and WHM Linux environment, message processing is partitioned between two core services: Exim, which functions as the Message Transfer Agent (MTA), and Dovecot, which functions as the Mail Delivery Agent (MDA) and IMAP/POP3 server.
The Message Lifecycle: Inbound and Outbound Pathways
When an external sender transmits a message to your corporate domain (e.g., [email protected]), the transaction proceeds through the following sequential stages:
- DNS Resolution: The sender’s MTA performs a DNS query for the target domain’s MX (Mail Exchange) record to locate the authoritative mail host (e.g.,
mail.company.com). - Perimeter SMTP Handshake: The remote MTA establishes a TCP handshake on port 25 with your server’s Exim listener. Exim evaluates Access Control Lists (ACLs), checks DNSBL (DNS Blacklists such as Spamhaus ZEN), validates Reverse DNS (PTR), and performs sender address verification.
- Content & Anti-Spam Heuristics: If accepted, the raw RFC 5322 payload is passed through local filtering pipelines (Apache SpamAssassin or Rspamd) and anti-virus scanners (ClamAV) to generate heuristic risk scores.
- Local Delivery Hand-off: Exim identifies the recipient as local, routes the stream to the local delivery transport (Dovecot LDA or LMTP), and commits the message payload to the recipient’s Maildir directory on disk.
- Client Retrieval: The end user’s mail client (Microsoft Outlook, Apple Mail, or Thunderbird) retrieves the message via encrypted IMAP over port 993, reading metadata directly from Dovecot’s pre-computed index cache.
Architecture Note: Never allow legacy plaintext protocols (POP3 port 110, IMAP port 143, or unauthenticated SMTP port 25) in production. Modern security postures mandate strict Implicit TLS (IMAP port 993, SMTP Submission port 465) or explicit STARTTLS (port 587) with high-cipher suites (ECDHE-ECDSA-AES256-GCM-SHA384 / TLS_AES_256_GCM_SHA384) to eliminate man-in-the-middle credential harvesting.
Storage Format Mechanics: Maildir vs. Legacy Mbox
Early Unix mail systems utilized the monolithic mbox format, wherein all messages inside a folder were appended sequentially to a single flat text file. This design caused severe filesystem locking conflicts, memory spikes, and catastrophic mailbox corruption whenever multiple processes attempted simultaneous read/write operations. In contrast, modern cPanel deployments utilize Maildir (and Maildir++ directory hierarchies). Under Maildir, every individual message is stored as an independent, immutable file across three subdirectories:
tmp/: Holds messages currently being written by the delivery agent to prevent partial reads.new/: Stores newly arrived messages that have not yet been queried or read by any client application.cur/: Contains messages that have been inspected by the client, with IMAP flags (Read, Flagged, Replied) encoded directly into the filename suffix (e.g.,:2,Sfor Seen).
Because Maildir relies on atomic POSIX link() and rename() operations, it completely eliminates lock contention. When deployed on high-IOPS Enterprise NVMe storage on MeraHost Enterprise Cloud, Dovecot can parse and search corporate mailboxes containing tens of thousands of messages in under 15 milliseconds.
2. Step-by-Step Mailbox Provisioning & Storage Quota Engineering
Provisioning corporate mailboxes requires establishing clear naming conventions, robust credential entropy, and deterministic quota policies. Follow these architectural steps within the cPanel administrative ecosystem:
Step 1: Navigating to Account Provisioning
Log in to your authenticated cPanel dashboard and locate the Email category. Click on the Email Accounts module. From the management overview table, click the blue + Create button on the right-hand panel.
Step 2: Domain Binding and Username Construction
Select your designated primary corporate domain from the Domain dropdown menu. Under Username, input the standard corporate alias (e.g., john.doe, billing, or support). Avoid ambiguous single-character or generic names that attract automated dictionary brute-force spam attacks.
Step 3: Cryptographic Password Enforcement
Select Set password now. Generate a cryptographically random string of at least 18 characters combining uppercase letters, lowercase letters, numbers, and special symbols. In cPanel, the built-in password strength meter must register 100/100. Automated bots continuously scan port 587 using dictionary lists; weak passwords represent the primary vector for unauthorized SMTP relay hijacking.
Step 4: Storage Quotas and Inode Boundaries
Click Edit Settings to configure advanced parameters:
- Storage Space: Specify a concrete quota (e.g.,
5120 MBor10240 MB) rather than selecting “Unlimited”. Setting explicit quotas protects Linux filesystem inode capacity and prevents a single compromised account from exhausting all disk space. - Folder Purge Rules: Enable automated deletion for trash and spam items older than 30 or 60 days to prevent abandoned accounts from accumulating stale disk overhead.
- Send Welcome Email: Select this option to automatically dispatch mail client configuration scripts and connection parameters to the user’s alternate inbox.
3. Production Performance Comparison Matrix
The operational gap between a default, out-of-the-box cPanel shared hosting setup and an enterprise-tuned, hardened production mail node is vast. The comparative matrix below highlights key infrastructure benchmarks:
| Feature / Metric | Standard / Default | Tuned / Production |
|---|---|---|
| Storage Engine & FS | Legacy mbox / Slow HDD | Maildir++ on Enterprise NVMe |
| Cryptographic Auth | Basic SPF Only (~all) | SPF (-all) + 2048-bit DKIM + Strict DMARC (p=reject) |
| Submission Security | Plaintext Port 25 / 110 allowed | Mandatory TLS 1.3 on 465 (SMTPS) & 993 (IMAPS) |
| Spam Filtering Daemon | SpamAssassin score 5.0 (static) | Rspamd Heuristics + Pyzor/Razor2 + Redis cache |
| Outbound Rate Limiting | Uncapped or static 50/hour | Granular Exim ACL token bucket with burst dampening |
| Inbox Placement Rate | 60% – 75% (frequent quarantine) | 99.8% Deterministic Inbox Delivery |
4. The Cryptographic Authentication Trifecta: SPF, DKIM, and DMARC
The single most critical reason business emails land in spam folders is the absence or misconfiguration of DNS cryptographic validation records. In 2024 and 2026 standards, major mailbox providers like Gmail, Yahoo, and Outlook categorically reject or isolate unauthenticated business domains. You must configure three interlocking DNS records in your domain’s Zone Editor:
Pillar 1: SPF (Sender Policy Framework – RFC 7208)
SPF allows domain owners to publish an authoritative whitelist of IP addresses and server hostnames permitted to transmit emails on behalf of their domain envelope. In cPanel, navigate to Email Deliverability to inspect your domain’s SPF record. A hardened production SPF record must resolve with a hard-fail (-all) or explicit soft-fail (~all):
; DNS TXT Record for SPF Authorization
; Host: @ (or example.com)
; Record Type: TXT
; Value:
v=spf1 +a +mx +ip4:198.51.100.25 include:_spf.merahost.org -all
In this syntax, +a and +mx permit your server’s primary web and mail IP addresses; +ip4:198.51.100.25 explicitly binds your dedicated outbound mail IP; and -all instructs remote MTAs to immediately reject any packet originating from an IP not listed in this directive.
Pillar 2: DKIM (DomainKeys Identified Mail – RFC 6376)
While SPF verifies the transmitting IP address, DKIM provides cryptographic integrity for the message payload itself. Exim computes a SHA-256 hash of the email headers and body, encrypts the hash using the domain’s private RSA key (stored securely in /var/cpanel/domain_keys/private/), and inserts a DKIM-Signature header into the outbound email. The receiving server fetches the public key from your DNS zone to decrypt and verify the hash.
Ensure that cPanel generates a modern 2048-bit RSA key (legacy 1024-bit keys are deemed insecure by modern cryptanalysis standards):
; DNS TXT Record for 2048-bit DKIM Key
; Host: default._domainkey.example.com
; Record Type: TXT
; Value:
v=DKIM1; k=rsa; p=MIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKCAQEAz8qF...IDAQAB
Pillar 3: DMARC (Domain-based Message Authentication – RFC 7489)
DMARC binds SPF and DKIM together by enforcing Identifier Alignment. It dictates what action a remote mail server must take if an email claiming to be from your domain fails SPF or DKIM checks. Furthermore, DMARC enables aggregate telemetry reporting so you receive daily XML reports detailing all outbound mail sent under your domain worldwide.
; Hardened Production DMARC Policy
; Host: _dmarc.example.com
; Record Type: TXT
; Value:
v=DMARC1; p=reject; sp=reject; pct=100; aspf=r; adkim=r; rua=mailto:[email protected]; ruf=mailto:[email protected]; fo=1
Architecture Note on DMARC Rollout: When introducing DMARC to an existing organization, avoid deploying
p=rejectimmediately. Follow a staged migration strategy: start withp=none(monitoring only) for 14 days to parseruareports and identify legitimate third-party senders (e.g., Zendesk, QuickBooks, or Mailchimp). Next, transition top=quarantine; pct=50, and finally lock the domain down withp=reject; pct=100.
5. Production Server Configuration & Kernel Optimization
For systems administrators running dedicated or VPS instances backing cPanel environments, optimizing server-level network buffers, socket backlog queues, and Dovecot memory limits is essential for sustained throughput under heavy concurrent IMAP syncing workloads.
Linux Kernel Tuning: /etc/sysctl.d/99-mail-performance.conf
High-volume email servers open and close thousands of short-lived TCP sockets per minute. Deploy the following kernel optimization parameters to prevent socket starvation, reduce TIME_WAIT churn, and expand TCP window buffers:
# /etc/sysctl.d/99-mail-performance.conf
# Kernel network tuning for high-throughput Exim & Dovecot mail servers

# Increase maximum TCP backlog queue
net.core.somaxconn = 4096
net.ipv4.tcp_max_syn_backlog = 8192

# Expand network interface packet reception queue
net.core.netdev_max_backlog = 10000

# Reuse TIME_WAIT sockets for fast TLS handshake turnaround
net.ipv4.tcp_tw_reuse = 1
net.ipv4.tcp_fin_timeout = 15

# Expand dynamic port range for outbound SMTP relay connections
net.ipv4.ip_local_port_range = 10240 65535

# TCP memory tuning for high-bandwidth IMAP attachment transfers
net.core.rmem_max = 16777216
net.core.wmem_max = 16777216
net.ipv4.tcp_rmem = 4096 87380 16777216
net.ipv4.tcp_wmem = 4096 65536 16777216

# Enable TCP BBR congestion control algorithm for minimal latency
net.core.default_qdisc = fq
net.ipv4.tcp_congestion_control = bbr
Apply these kernel parameters immediately by executing sysctl --system in your root terminal.
Hardened Dovecot IMAP/POP3 Configuration Snippet
Within WHM or custom Dovecot drop-in configuration templates (/etc/dovecot/dovecot.conf), apply the following performance directives to enable in-memory mailbox index caching, SSL session reuse, and worker process recycling:
# Production Dovecot Optimization Block
# Enhanced concurrent connection handling and memory-mapped indexes

# Enforce modern TLS protocol standards
ssl = required
ssl_min_protocol = TLSv1.2
ssl_cipher_list = ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384
ssl_prefer_server_ciphers = yes

# Mailbox memory-mapped index cache settings
default_process_limit = 512
default_client_limit = 2048

service imap-login {
  process_min_avail = 4
  client_limit = 500
  service_count = 0
}

# Inode and idle connection cleanup
imap_idle_notify_interval = 29 mins
mail_max_userip_connections = 64
6. Client Configuration & Automatic Discovery Protocols
Once the mailbox and DNS cryptographic records are established, end users must configure desktop and mobile email applications. Modern cPanel environments offer native support for Autodiscover (Microsoft Outlook) and Autoconfig (Mozilla Thunderbird, Apple Mail), allowing clients to determine connection endpoints automatically simply by entering their email address and password.
Standard Manual Connection Parameters
If a client application requires manual setup, always enforce secure encrypted parameters:
- Incoming Server (IMAP):
mail.yourdomain.com| Port:993| Encryption:SSL/TLS - Outgoing Server (SMTP):
mail.yourdomain.com| Port:465(SSL/TLS) or587(STARTTLS) - Authentication: Required for both incoming and outgoing connections; username is the full email address (e.g.,
[email protected]).
DNS SRV Records for Zero-Touch Provisioning
To guarantee seamless zero-touch provisioning across iOS, Android, and macOS mail apps, configure the following SRV resource records in your domain’s DNS zone:
; Service Discovery SRV Records for Secure Email Auto-Configuration
_imaps._tcp.example.com.    3600    IN    SRV    0    1    993    mail.example.com.
_smtps._tcp.example.com.    3600    IN    SRV    0    1    465    mail.example.com.
_submission._tcp.example.com. 3600  IN    SRV    0    1    587    mail.example.com.
7. Frequently Asked Questions (Enterprise Mail Operations)
Why do my emails go to Gmail’s Spam folder even after setting up SPF and DKIM?
While SPF and DKIM authenticate your identity, inbox placement depends equally on three additional factors: Reverse DNS (PTR) alignment, DMARC identifier alignment, and IP reputation warm-up. If your server’s sending IP lacks a matching PTR record that resolves back to your mail host (e.g., mail.example.com), or if you send sudden high volumes from a newly provisioned IP without gradual volume warm-up, Google’s adaptive spam filters will automatically route messages to spam. Ensure your PTR matches your server’s HELO/EHLO hostname perfectly.
Should I choose POP3 or IMAP for our corporate business mailboxes?
For virtually all modern enterprise environments, IMAP (Internet Message Access Protocol) is the mandatory choice. IMAP maintains bidirectional state synchronization between the server and all connected client devices (laptops, tablets, mobile phones), preserving read flags, folders, and sent items. POP3 downloads messages to a single local device and deletes them from the server by default, destroying multi-device synchronization and leaving communications vulnerable to local hardware loss without centralized server backups.
Can I host my website on cPanel while routing emails through Google Workspace or Microsoft 365?
Yes. This hybrid architecture is common in corporate deployments. In cPanel, navigate to the Zone Editor and replace your local MX record with Google Workspace or Microsoft 365 MX endpoints. Crucially, you must also navigate to Email Routing inside cPanel and change the routing mode from Local Mail Exchanger to Remote Mail Exchanger. This prevents cPanel’s local Exim daemon from intercepting emails sent via web contact forms and forces all outbound traffic to query external DNS.
How does Maildir storage prevent mailbox corruption compared to legacy mbox?
Maildir organizes every individual email message as an independent file on the Linux filesystem rather than concatenating all messages into a single monolithic document. Delivery agents write new incoming messages into a temporary directory (tmp/) and atomically move them into new/ using POSIX rename system calls. This eliminates file-locking contention entirely, ensuring that simultaneous client reads and delivery writes never corrupt mailbox structures or trigger data loss.
For mission-critical production environments where transactional velocity, high email deliverability, and guaranteed server uptime are non-negotiable, hosting your business infrastructure on MeraHost Enterprise Cloud delivers dedicated enterprise NVMe storage arrays, pure LiteSpeed Web Server execution, and predictable long-term budgeting with zero renewal price hikes.
Deploy Enterprise-Grade Production Infrastructure
Need guaranteed performance with zero price hikes? Host mission-critical workloads on MeraHost with pure Enterprise NVMe, LiteSpeed Web Server, and Same Renewal Price, Always (starting at ₹99/mo).