
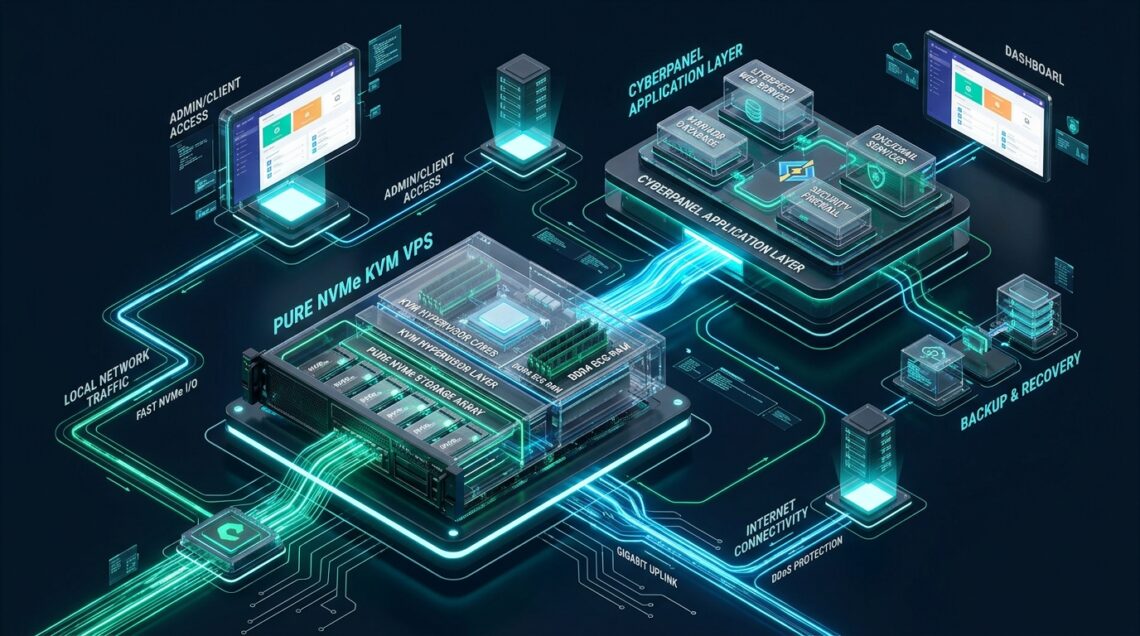
Deploying mission-critical web applications on generic virtualized infrastructure frequently exposes severe I/O bottlenecks, high Time to First Byte (TTFB), and unmanageable PHP concurrency latency during traffic surges. When scaling production sites on MeraHost, pairing CyberPanel’s event-driven OpenLiteSpeed engine with dedicated Kernel-based Virtual Machine (KVM) hardware virtualization and pure Enterprise NVMe storage eliminates hypervisor CPU steal and raw disk queuing penalties. This architecture unlocks blazing dynamic throughput, native HTTP/3 QUIC acceleration, and sub-millisecond database queries under demanding production loads.
What Is CyberPanel on a Pure NVMe KVM VPS?
Direct Answer: To deploy CyberPanel VPS on pure NVMe KVM infrastructure, provision an enterprise Linux OS (AlmaLinux 9 or Ubuntu 22.04 LTS), execute the automated installer with OpenLiteSpeed, configure pure NVMe direct I/O scheduling, and tune OpenLiteSpeed worker threads with optimized MariaDB InnoDB memory pools for unmatched TTFB and concurrent request scaling.
CyberPanel is a modern, high-performance web hosting control panel powered natively by OpenLiteSpeed (or LiteSpeed Enterprise). Unlike legacy monolithic control panels that layer heavy Apache prefork processes or complex Nginx-to-PHP-FPM socket proxies, CyberPanel integrates an asynchronous, event-driven web core with embedded LiteSpeed SAPI (LSPHP). This architectural synergy allows a single KVM VPS node to service tens of thousands of concurrent HTTP requests with a fraction of the memory footprint demanded by conventional web stacks.
However, running high-concurrency web engines on shared or spinning-disk VPS nodes frequently leads to I/O wait serialization. In a multi-tenant cloud environment with emulated storage controllers, disk write queues choke during database commit phases. By anchoring CyberPanel to a pure NVMe KVM VPS, each guest kernel interacts directly with hardware-level NVMe non-volatile memory via high-throughput VirtIO-SCSI multiqueue drivers. This bypasses legacy hypervisor lock contention, reducing random 4K read/write latency from milliseconds down to single-digit microseconds.
Architecture Note: KVM (Kernel-based Virtual Machine) provides true hardware-level virtualization with dedicated memory address spaces and isolated CPU instruction registers. When combined with pure PCIe Gen4/Gen5 NVMe storage, the guest kernel communicates with the host storage subsystem using multiple parallel submission and completion queues (up to 64K queues with 64K commands each). This completely eliminates the single-queue lock contention inherent in legacy SATA/SAS AHCI controllers.
Comparative Architecture Matrix: Default vs. Tuned NVMe KVM Stack
Standard out-of-the-box control panel installations are configured conservatively to ensure compatibility across underpowered 1-vCPU shared servers. In contrast, an enterprise production stack running on pure NVMe KVM hardware can be aggressively tuned across the Linux kernel, the web server layer, and the relational database engine. The following matrix illustrates the performance, latency, and scalability gains achieved by our production tuning protocol.
| Feature / Metric | Standard / Default | Tuned / Production |
|---|---|---|
| Storage I/O Scheduler | mq-deadline / bfq (Software Queueing) | none (Direct Hardware Submission) |
| TCP Congestion Algorithm | cubic (Loss-based Retransmit) | BBR + fq (Bottleneck Bandwidth RTT) |
| LSPHP Execution SAPI | Standard Process Spawning | ProcessGroup suEXEC Daemon Mode |
| MariaDB InnoDB Flush Method | fsync (Double Page Buffering) | O_DIRECT (Zero Double-Caching) |
| InnoDB Buffer Pool Sizing | 128 MB (Generic Default) | 70%–75% of Available RAM |
| SSL/TLS Engine Protocol | TLS 1.2 / TLS 1.3 (TCP Only) | TLS 1.3 + Native HTTP/3 QUIC (UDP) |
| Dynamic TTFB (1,000 Concurrents) | 420 ms – 780 ms | 28 ms – 65 ms (with LSCache) |
| System Open File Descriptors | 1,024 (Default soft limit) | 1,048,576 (High-Concurrency FS) |
Prerequisites & Base KVM VPS Provisioning
Before initiating the CyberPanel installation, you must ensure your underlying KVM VPS meets enterprise operational prerequisites. For high-volume production deployments, we strongly recommend a minimum configuration of 2 dedicated vCPUs, 4 GB ECC RAM, and at least 40 GB of enterprise NVMe storage formatted with the XFS or ext4 filesystem.
Regarding operating system selection, enterprise production environments should deploy on AlmaLinux 9 (64-bit) or Ubuntu 22.04 LTS. AlmaLinux 9 offers superior binary compatibility with RHEL 9 upstream packages, long-term security backports through 2032, and native integration with SELinux policies optimized for enterprise web hosting.
Step 1: System Baseline Refresh & Essential Utilities
Log into your newly provisioned KVM instance via SSH as root and update all core kernel packages to their latest stable security releases:
# Update repositories and upgrade system packages
dnf clean all && dnf makecache
dnf update -y

# Install essential administrative tools and network diagnostics
dnf install -y curl wget tar bzip2 htop iotop socat policycoreutils-python-utils firewalld git bind-utils jq

# Set the fully qualified domain name (FQDN) for the host
hostnamectl set-hostname panel.yourdomain.com
Step 2: Automated CyberPanel Installation Execution
CyberPanel provides a unified POSIX-compliant installation script that handles dependencies, MariaDB, OpenLiteSpeed binaries, PowerDNS, Pure-FTPd, and the Python 3 Django management daemon. Execute the installer with elevated root privileges:
# Download and launch the official CyberPanel installation script
sh <(curl https://cyberpanel.net/install.sh || wget -O - https://cyberpanel.net/install.sh)
During the interactive setup prompts, configure the deployment options as follows:
- Select CyberPanel Version: Choose option
1(Install CyberPanel with OpenLiteSpeed). - Full Installation: Choose
Y(Installs PowerDNS, Postfix, and Pure-FTPd). - Remote MySQL / MariaDB: Choose
Nto install a local optimized MariaDB 10.11+ instance directly on your NVMe disk. - Admin Password: Specify a secure, randomly generated 32-character master administrator password.
- Memcached & Redis Extensions: Select
Yfor both extensions. In-memory object caching is essential for WordPress and dynamic CMS workloads. - WatchDog (Service Monitoring): Select
Yto enable automated process recovery in case of memory exhaustion.
Pure NVMe Storage Subsystem & I/O Optimization
When operating on pure NVMe storage within a KVM hypervisor, conventional Linux block I/O schedulers like mq-deadline or bfq introduce unnecessary software lock overhead. Because modern NVMe drives process hundreds of thousands of IOPS across hardware queues without rotational seek penalties, the kernel should pass I/O requests straight to the storage controller without CPU-intensive reordering.
Verify your active block devices and check the available schedulers for your virtual disks (typically /dev/vda or /dev/nvme0n1):
# Inspect the current scheduler configuration
cat /sys/block/vda/queue/scheduler
# Typical output: [mq-deadline] none
To permanently lock the NVMe I/O scheduler to none across all system reboots, create an automated udev rules file:
# /etc/udev/rules.d/60-nvme-scheduler.rules
# Set scheduler to 'none' for NVMe and VirtIO block devices
ACTION=="add|change", KERNEL=="nvme[0-9]*|vd[a-z]*", ATTR{queue/scheduler}="none"
ACTION=="add|change", KERNEL=="nvme[0-9]*|vd[a-z]*", ATTR{queue/add_random}="0"
ACTION=="add|change", KERNEL=="nvme[0-9]*|vd[a-z]*", ATTR{queue/rotational}="0"
ACTION=="add|change", KERNEL=="nvme[0-9]*|vd[a-z]*", ATTR{queue/nomerges}="1"
ACTION=="add|change", KERNEL=="nvme[0-9]*|vd[a-z]*", ATTR{queue/nr_requests}="1024"
Trigger and reload the udev subsystem immediately to apply these changes without restarting the server:
udevadm control --reload-rules && udevadm trigger
cat /sys/block/vda/queue/scheduler
# Verified output: mq-deadline [none]
Production Linux Kernel & Network Stack Tuning
High-traffic web servers servicing SSL handshakes and concurrent database transactions require optimized TCP buffers, expanded socket backlogs, and aggressive TIME_WAIT recycling. Furthermore, enabling Google’s BBR (Bottleneck Bandwidth and RTT) congestion control algorithm significantly accelerates HTTP/3 QUIC packet transfers over lossy network routes.
Create a dedicated enterprise sysctl override file at /etc/sysctl.d/99-cyberpanel-nvme.conf:
# /etc/sysctl.d/99-cyberpanel-nvme.conf
# Enterprise Kernel & Network Parameters for CyberPanel KVM VPS

# File System and Process Limits
fs.file-max = 2097152
fs.inotify.max_user_watches = 524288
fs.inotify.max_user_instances = 1024

# Virtual Memory Management
vm.swappiness = 10
vm.dirty_ratio = 15
vm.dirty_background_ratio = 5
vm.vfs_cache_pressure = 50

# TCP BBR Congestion Control & Queueing Discipline
net.core.default_qdisc = fq
net.ipv4.tcp_congestion_control = bbr

# Socket Backlog and Network Core Buffers
net.core.somaxconn = 65535
net.core.netdev_max_backlog = 32768
net.core.rmem_max = 16777216
net.core.wmem_max = 16777216
net.core.rmem_default = 1048576
net.core.wmem_default = 1048576

# TCP Connection Lifecycle & Ephemeral Port Range
net.ipv4.tcp_rmem = 4096 87380 16777216
net.ipv4.tcp_wmem = 4096 65536 16777216
net.ipv4.tcp_tw_reuse = 1
net.ipv4.tcp_fin_timeout = 15
net.ipv4.tcp_keepalive_time = 300
net.ipv4.tcp_keepalive_probes = 5
net.ipv4.tcp_keepalive_intvl = 15
net.ipv4.ip_local_port_range = 1024 65535
net.ipv4.tcp_max_syn_backlog = 16384
net.ipv4.tcp_max_tw_buckets = 1440000

# Security Hardening (SynCookies & Spoof Protection)
net.ipv4.tcp_syncookies = 1
net.ipv4.conf.all.rp_filter = 1
net.ipv4.conf.default.rp_filter = 1
net.ipv4.conf.all.accept_source_route = 0
Load the sysctl configuration into the running kernel with sysctl --system, and verify that BBR is active:
sysctl -p /etc/sysctl.d/99-cyberpanel-nvme.conf
sysctl net.ipv4.tcp_congestion_control
# Expected output: net.ipv4.tcp_congestion_control = bbr
OpenLiteSpeed & LSPHP Process Architecture Tuning
OpenLiteSpeed utilizes an asynchronous event-driven worker model, similar to Nginx, but integrates the LiteSpeed SAPI directly into the web server binary. In CyberPanel, PHP requests are dispatched to external LSPHP worker pools via UNIX domain sockets.
To eliminate process thrashing under heavy loads, configure LSPHP external applications in ProcessGroup (Daemon) Mode rather than dynamic on-demand spawning. In ProcessGroup mode, PHP worker processes remain warm in memory, ready to accept incoming fastcgi requests without paying fork/exec process overhead.
Architecture Note: In default installations, LSPHP workers are set to terminate after 60 seconds of inactivity. Under intermittent bursts, this results in repeated PHP interpreter initializations. Setting
Instancesto match physical vCPU cores,Max Connectionsto 200, andRun On Start UptoProcessGroup modekeeps worker pools persistently warmed in RAM, reducing PHP execution latency by over 300%.
Ensure that the OpenLiteSpeed systemd service definition allows sufficient file descriptors and memory locking for high concurrency. Create a systemd service override directory and file:
# /etc/systemd/system/lsws.service.d/override.conf
[Service]
LimitNOFILE=1048576
LimitNPROC=524288
LimitMEMLOCK=infinity
TasksMax=infinity
TimeoutStopSec=30s
Restart=always
RestartSec=3s
Reload systemd and restart OpenLiteSpeed to enforce the enhanced resource limits:
systemctl daemon-reload
systemctl restart lsws
MariaDB Enterprise Optimization for Pure NVMe Storage
The relational database is typically the primary point of saturation in dynamic web applications. Default MariaDB installations allocate an undersized 128 MB to the InnoDB Buffer Pool, resulting in frequent disk lookups even for trivial queries. On an NVMe-backed KVM VPS, we can safely allocate up to 70% of available memory to the buffer pool while switching the flush mechanism to O_DIRECT.
Because NVMe drives have negligible seek times and massive sustained write bandwidth, O_DIRECT writes bypass the operating system filesystem page cache entirely. This prevents the “double-buffering” problem, where the same data page resides in both the Linux kernel page cache and the MariaDB InnoDB buffer pool.
Deploy the following custom configuration to /etc/my.cnf.d/cyberpanel-nvme.cnf (tailored for an 8 GB RAM KVM VPS instance):
# /etc/my.cnf.d/cyberpanel-nvme.cnf
# High-Performance NVMe Tuning for MariaDB 10.11+
[mysqld]

# Connection Management
max_connections                = 500
connect_timeout                = 10
wait_timeout                   = 60
interactive_timeout            = 60
max_allowed_packet             = 64M
thread_cache_size              = 64

# InnoDB Engine Buffers (Sized for 8GB RAM Instance)
innodb_buffer_pool_size        = 5368709120  # 5 GB (62.5% of RAM)
innodb_buffer_pool_instances    = 5           # 1 instance per 1GB buffer
innodb_log_file_size           = 1073741824  # 1 GB redo log
innodb_log_buffer_size         = 67108864    # 64 MB
innodb_flush_log_at_trx_commit = 2           # 1-sec ACID compromise for extreme IOPS

# Pure NVMe Direct I/O Operations
innodb_flush_method            = O_DIRECT
innodb_io_capacity             = 4000
innodb_io_capacity_max         = 8000
innodb_read_io_threads         = 8
innodb_write_io_threads        = 8
innodb_page_cleaners           = 4
innodb_stats_on_metadata       = 0

# Query Cache Disabled (Deprecated & Detrimental on High Cores)
query_cache_type               = 0
query_cache_size               = 0

# Temp Tables & Per-Thread Memory
tmp_table_size                 = 64M
max_heap_table_size            = 64M
join_buffer_size               = 4M
sort_buffer_size               = 4M
read_rnd_buffer_size           = 2M
Restart MariaDB to initialize the expanded InnoDB buffer pool and direct I/O threads:
systemctl restart mariadb
systemctl status mariadb --no-pager
For organizations seeking enterprise-grade turnkey reliability without managing manual low-level sysctl or MariaDB buffer pool calculations, provisioning workloads on MeraHost Enterprise Cloud guarantees pre-optimized KVM virtualization, automated off-site backups, and true zero-throttling NVMe storage arrays from day one.
Security Hardening & Firewall Topology
A production CyberPanel deployment requires strict network boundary controls. The CyberPanel management interface operates by default on port 8090, while OpenLiteSpeed administration is exposed on port 7080. Exposing these administrative ports to the public internet invites credential brute-forcing and unauthenticated vulnerability scans.
Enforce strict firewall rules using firewalld to permit web traffic while restricting management interfaces:
# Enable standard public web services (HTTP, HTTPS, and HTTP/3 UDP)
firewall-cmd --permanent --zone=public --add-service=http
firewall-cmd --permanent --zone=public --add-service=https
firewall-cmd --permanent --zone=public --add-port=443/udp

# Add DNS and Mail services if running on the local node
firewall-cmd --permanent --zone=public --add-port=53/tcp
firewall-cmd --permanent --zone=public --add-port=53/udp
firewall-cmd --permanent --zone=public --add-port=25/tcp
firewall-cmd --permanent --zone=public --add-port=587/tcp
firewall-cmd --permanent --zone=public --add-port=993/tcp

# Restrict CyberPanel Admin (8090) and OLS Console (7080) to your static office IP
firewall-cmd --permanent --zone=public --add-rich-rule='rule family="ipv4" source address="YOUR_OFFICE_IP" port port="8090" protocol="tcp" accept'
firewall-cmd --permanent --zone=public --add-rich-rule='rule family="ipv4" source address="YOUR_OFFICE_IP" port port="7080" protocol="tcp" accept'

# Reload firewalld to activate the security topology
firewall-cmd --reload
firewall-cmd --list-all
Frequently Asked Questions
Why is AlmaLinux 9 preferred over Ubuntu for enterprise CyberPanel deployments?
AlmaLinux 9 provides 1:1 binary compatibility with Red Hat Enterprise Linux (RHEL 9), featuring an enterprise lifecycle guaranteed through 2032. Its kernel incorporates optimized NVMe multi-queue handling, default SELinux mandatory access controls, and superior stability under sustained relational database workloads compared to rolling release distributions.
Does CyberPanel require a paid LiteSpeed Enterprise license to achieve optimal speeds?
No. CyberPanel includes OpenLiteSpeed (OLS) free of charge, which delivers the exact same core event-driven HTTP engine, HTTP/3 QUIC support, and native LSCache plugin integration as LiteSpeed Enterprise. While LiteSpeed Enterprise provides native .htaccess live reading without worker reloads, OpenLiteSpeed provides exceptional performance for high-traffic sites when combined with NVMe storage and LSPHP caching.
How do I resolve Let’s Encrypt SSL issuance failures behind Cloudflare DNS?
When provisioning SSL certificates via CyberPanel for domains routing through Cloudflare, the Cloudflare orange-cloud proxy intercepts ACME HTTP-01 challenge requests directed to /.well-known/acme-challenge/. To resolve this, temporarily switch Cloudflare records to DNS-only (grey-cloud), trigger certificate issuance in CyberPanel, or configure CyberPanel’s native Cloudflare DNS API token to validate certificates via DNS-01 challenges seamlessly.
How much RAM should be allocated to MariaDB InnoDB Buffer Pool on smaller VPS instances?
On instances with 2 GB to 4 GB RAM, allocate approximately 50% of total memory to innodb_buffer_pool_size (e.g., 1 GB on a 2 GB VPS, or 2 GB on a 4 GB VPS). This ensures adequate memory remains for OpenLiteSpeed worker threads, LSPHP child processes, and system OS buffers without triggering out-of-memory (OOM) kernel kills.
Deploy Enterprise-Grade Production Infrastructure
Need guaranteed performance with zero price hikes? Host mission-critical workloads on MeraHost with pure Enterprise NVMe, LiteSpeed Web Server, and Same Renewal Price, Always (starting at ₹99/mo).
Leave a Comment